TL;DR

Get wellness gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
The Pragmatic Engineer published an interview with Sean Allen, a distinguished engineer at Antithesis, about software correctness and supply chain security. Allen discusses using invariants and repeatable workloads to find failures, and says there is no single or simple fix for attacks involving compromised software packages.
The Pragmatic Engineer has published an interview with Sean Allen, a distinguished engineer at Antithesis, examining how software teams can reason about correctness and reduce the risk of failures. Allen argues for specifying expected behavior through invariants and repeatedly exercising realistic workloads, while warning that software supply chain attacks have no single, simple defense.
Allen defines correctness in practical terms: whether a program does what its users or operators expect. In the interview, he describes an invariant as a guarantee about software behavior, while pointing out that teams may not know the full specification in advance. He says software can be considered “correct enough” when it fulfills its business purpose and does not cause an overnight outage.
The conversation challenges the idea that testing alone can establish correctness. Allen favors designing systems so that invalid states are difficult or impossible to express, and says developers should use validation techniques early rather than rely on quality checks added as late-stage CI/CD gates. He also discusses “workloads” that can be run repeatedly to expose failures, including the Bank Test, which is used to stress database isolation guarantees.
On supply chain security, Allen describes a difficult trade-off: packages can be hijacked and used to execute malicious code on machines or services, but the strongest language-level defenses are not widely adopted, while popular languages often assume a trustworthy software ecosystem. The report presents this as Allen’s assessment, not as evidence that any particular package or service was compromised. The interview also covers type systems, the Pony language, garbage collection, technical debt and the value of spending more time on design and alignment.
Correctness Before Code Ships
The discussion matters to engineering teams because software failures can affect service availability, data integrity and users, while compromised dependencies can introduce malicious behavior through tools developers already rely on. Allen’s emphasis on invariants and repeated workloads points to ways teams can look for failures beyond a narrow set of hand-written test cases.
His comments also highlight that security depends partly on design choices made across an ecosystem. A language may offer stronger protections, but those protections have limited reach if teams do not use it; meanwhile, widely used languages and package systems can expose developers to assumptions about trusted maintainers and dependencies. Allen does not offer a universal remedy, so the interview is best read as an engineering perspective on the limits of any single control.
Products Worth Considering

Garmin Forerunner 55 GPS Running Smartwatch, Black
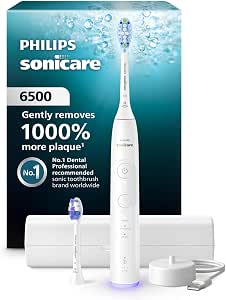
Philips Sonicare 6500 Series Rechargeable Electric Toothbrush with 2 Brush Heads, White

Bowflex SelectTech 840 Adjustable Kettlebell
As an affiliate, we earn on qualifying purchases.
The Interview’s Engineering Focus
The Pragmatic Engineer introduces Allen as an engineer experienced in large distributed systems, stream processing and confidential computing, and as a core contributor to Pony, a language designed for concurrency. The publication says his work on correctness at Antithesis prompted the conversation. It also discloses that Antithesis is a podcast sponsor, while stating that the interview itself was not sponsored.
The report frames the discussion around practical software development rather than a single product launch or security incident. Its topics include the contrast between strongly typed languages and other language traditions, alternatives to relying exclusively on unit tests, and the idea that technical debt does not always have to be repaid if a system is later rewritten. No specific new tool, vulnerability disclosure or policy change is announced in the supplied material.
““It’s down to whether my program does what I expect.””
— Sean Allen, distinguished engineer at Antithesis
Limits of the Security Advice
The supplied report does not set out a tested security plan, quantify the frequency or impact of package compromises, or identify a particular incident. Allen’s account of language-level defenses and ecosystem assumptions is an attributed expert view; the material does not compare specific languages or measure how much protection one approach provides.
It is also unclear from the supplied text how the proposed workload testing should be implemented across different kinds of systems, or what mix of testing and language safeguards Allen would recommend for a particular team. The report excerpt ends during the interview, so it may not contain every question or qualification in the full article.
No Fix or Launch Announced
The supplied report does not announce a follow-up study, product release or new security measure. Readers seeking Allen’s fuller reasoning can consult the complete Pragmatic Engineer interview; the publication also says the conversation is available to watch on YouTube. Any operational response remains a matter for individual engineering teams, based on their systems, dependencies and threat models.
Key Questions
What is the main development?
The Pragmatic Engineer published an interview with Sean Allen about software correctness, testing approaches and supply chain security. The source does not describe a new product or a specific breach.
How does Allen define software correctness?
He says correctness depends on whether software does what is expected of it. He discusses invariants as guarantees of behavior, while noting that teams do not always know the full expected behavior in advance.
What does Allen recommend instead of relying only on manual testing?
The report says Allen favors making invalid states difficult to express and exercising repeatable workloads to find failures. It does not present those methods as a universal replacement for all testing.
What does the interview say about supply chain attacks?
Allen characterizes defense as difficult because package compromise can lead to malicious code execution, while stronger language-level protections may be uncommon in practice. He says there is no single or simple fix; the report does not identify a particular attack.
Source: newsletter.pragmaticengineer.com